 Khushi Shaha
Why Seedless Fruit Exists — And What the Bill Gates Seed-Bank Claim Gets Wrong
A viral Instagram reel claims that seedless fruit is part of a deliberate plan to control the food supply, linking it to Bill Gates, seed banks, digital IDs, and the UN’s Agenda 2030. Each of those subjects is real. The problem is that the reel treats them as a single causal chain. They are not.
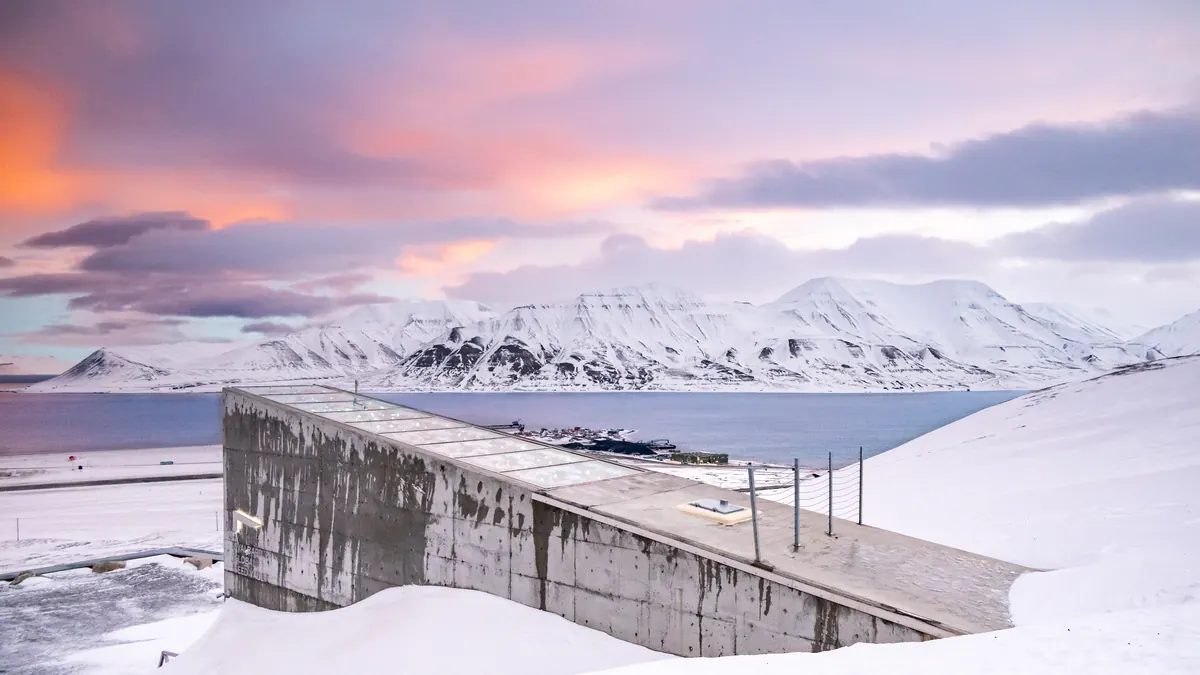
Seedless fruit can arise through several biological and horticultural mechanisms, including parthenocarpy, stenospermocarpy and, in crops such as seedless watermelon, triploidy. Parthenocarpy is the development of fruit without fertilization — occurring naturally in some species and induced in others through specific cultivation conditions. Triploid plants have three sets of chromosomes, which can make normal seed formation difficult or impossible; seedless watermelons are the most common commercial example. Many common seedless varieties are produced through conventional breeding or plant-development techniques rather than genetic modification. The Svalbard Global Seed Vault in Norway holds more than 1.4 million seed samples as a long-term backup for genebanks around the world. The Seed Vault is operated through a partnership involving Norway, NordGen and the Crop Trust; it is not owned or operated by the Gates Foundation.
The reel’s specific claim — that seedless fruit is part of a coordinated mechanism to remove people’s ability to grow their own food — does not match how seedless varieties are produced, distributed, or why they exist. Genuine food-security researchers study seed diversity, crop genetics, and the risks of agricultural monoculture; those are legitimate scientific topics. The claim that seedless fruit itself is the mechanism of control is a separate matter and is not supported by the horticultural record.
Why Seedless Fruit Does Not Remove Seed Access
The reel’s implied logic — no seeds in fruit means people cannot grow their own food — misunderstands how seedless varieties reproduce.
Seedless watermelons are grown from seeds. The seeds are sold commercially and planted each season to produce seedless fruit. The fruit has no viable seeds; the plant absolutely does. Seedless grapes are propagated through cuttings — a technique used by home gardeners and commercial growers for centuries that requires no seed at all, seedless or otherwise. Bananas, nearly all commercial varieties of which are seedless, have been reproduced through vegetative propagation for thousands of years without genetic modification.
Parthenocarpy describes fruit development without fertilization. A plant producing parthenocarpic fruit may still be propagated through seeds or vegetative methods depending on the species and variety. Triploid crops like commercial watermelons are grown from seeds produced by crossing diploid and tetraploid parent plants; those seeds are commercially available.
None of this requires a controlling authority. Home gardeners and smallholders grow seedless varieties from materials widely available through seed companies, nurseries, and agricultural suppliers.
What Agenda 2030 and the Svalbard Vault Actually Are
The UN’s Agenda 2030 — formally the 2030 Agenda for Sustainable Development — is a set of 17 Sustainable Development Goals adopted by 193 UN member states in 2015. Goal 2 addresses hunger and food security. The text of Agenda 2030 contains no reference to seedless fruit, no mechanism for controlling seed banks, and no provision relating to digital IDs in connection with food systems.
The Svalbard Global Seed Vault is a backup storage facility, not a vault that grants any party control over deposited material. Countries and seed conservation institutions deposit duplicates of their own collections there for safekeeping in the event of local disasters — a fire destroying a national genebank, for example. Depositors retain ownership of their seeds. The facility’s operations and depositor list are publicly documented by the Crop Trust.
Bill Gates’s charitable foundation has funded agricultural development programs in Sub-Saharan Africa and South Asia, including work with seed systems and crop research. That involvement is a matter of public record and a subject of legitimate policy debate. It is not the same as controlling the Svalbard facility, which neither the Gates Foundation nor any comparable private entity owns or operates.
There is no evidence that ordinary commercially sold seedless fruit is being used to secretly deliver vaccines. Plant-based vaccine research does exist, but it involves deliberate development and controlled production of plants or plant material designed to express a target antigen. It cannot happen through the production of ordinary seedless fruit sold in supermarkets.
Why some fruit is seedless, how seed banks work, and what the UN’s sustainable development agenda says are all publicly documented in primary sources. The Svalbard vault’s data is available at its official website. Agenda 2030’s full text is published by the UN. Readers interested in the actual science of crop genetics and food security can find primary research through the Food and Agriculture Organization and the Crop Trust.
———————————————————————————————–
———————————————————————————————–
## How to Log Into WordPress REST API — Step by Step
### What We Used: **Application Password Authentication**
—
### Step 1: Get the Credentials
From the Pipeline file (`Karmactive Pipeline.md`), the credentials are:
– **Username**: `Sunita Somvanshi`
– **Application Password**: `Tw8QKhc98KxU5L4O3Q0s0w6J` (remove spaces → `Tw8QKhc98KxU5L4O3Q0s0w6J`)
> Application Passwords are created in WordPress Admin → **Users → Profile → Application Passwords** section. They’re separate from the login password and designed for API access.
—
### Step 2: Test the Login (Verify It Works)
“`bash
curl -s -u “Sunita Somvanshi:Tw8QKhc98KxU5L4O3Q0s0w6J” \
“https://www.karmactive.com/wp-json/wp/v2/users/me?_fields=id,name”
“`
**Expected response**: `{“id”:57,”name”:”Sunita Somvanshi”}` ✅
—
### Step 3: Make Authenticated API Calls
**GET a post** (read):
“`bash
curl -s -u “Sunita Somvanshi:Tw8QKhc98KxU5L4O3Q0s0w6J” \
“https://www.karmactive.com/wp-json/wp/v2/posts/1779?_fields=id,title,author”
“`
**PATCH/UPDATE a post** (write):
“`bash
curl -s -X POST \
-u “Sunita Somvanshi:Tw8QKhc98KxU5L4O3Q0s0w6J” \
-H “Content-Type: application/json” \
-d ‘{“meta”:{“_yoast_wpseo_focuskw”:”your keyword here”}}’ \
“https://www.karmactive.com/wp-json/wp/v2/posts/1779”
“`
> Note: WordPress REST API uses `POST` for updates (not `PATCH`), even when editing existing posts.
—
### Step 4: Check the HTTP Response Code
– **200** = Success ✅
– **401** = Auth failed (wrong credentials)
– **403** = Forbidden (user doesn’t have permission)
– **404** = Post not found
—
### How It Works Under the Hood
“`
curl -u “username:app_password”
↓
WordPress sees Basic Auth header
↓
Checks Application Password table (not login password)
↓
Grants API access with that user’s role/capabilities
↓
Sunita = Editor role → can edit any post ✅
“`
—
### Why This Works Now (But Failed Before)
The previous sessions used:
– ❌ Regular WP login password → blocked by Cloudflare WAF
– ❌ Programmatic browser login → WAF blocks `POST /wp-login.php`
– ✅ **Application Password** → bypasses WAF, goes directly to REST API endpoint, which Cloudflare allows through
—