 Karmactive Team
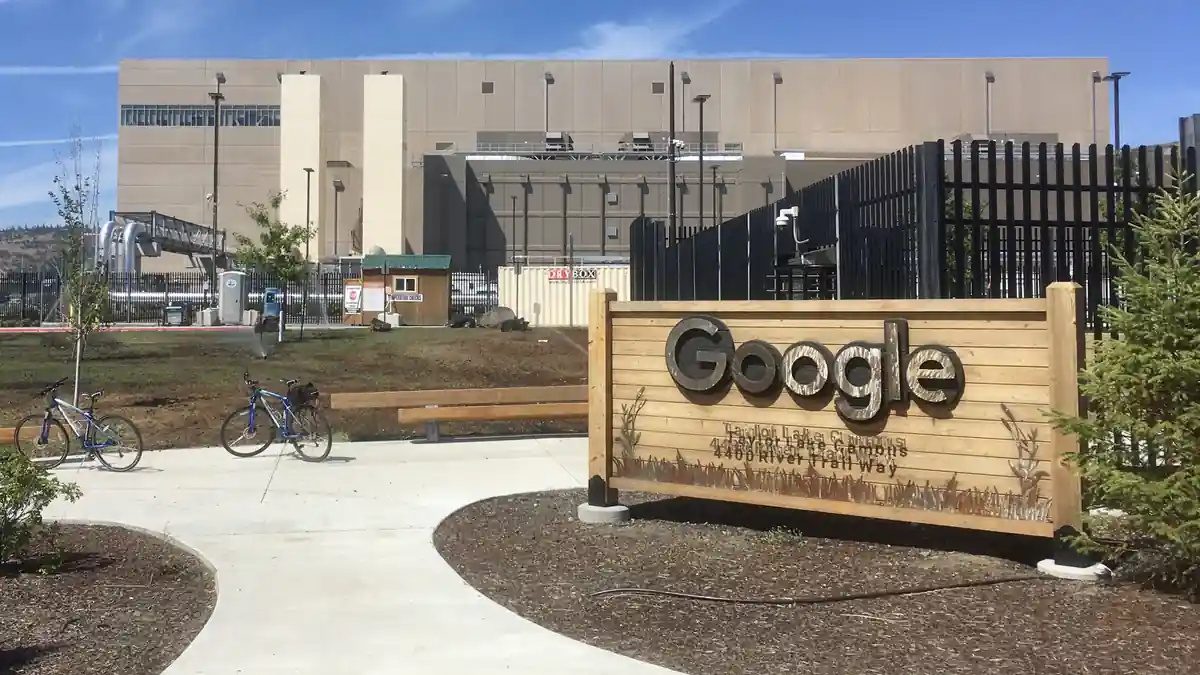
Google officially announced Gemini 4 Argon on September 30, but you can’t access it yet. The company is deliberately limiting its rollout to trusted cybersecurity defenders — and the reason has everything to do with what the model can actually do.
Google's DeepMind team announced Gemini 4 Argon through its official blog on September 30, 2026. The company reports strong benchmark performance across coding, finance, legal analysis, and cybersecurity tasks. Argon features a one-million-token context window — enabling it to process large-scale content, including codebases, within a single session. Pricing is set at $2 per million input tokens and $10 per million output tokens for organizations that gain access. The model is currently available only to participants in Google’s Fairwind Program, a restricted initiative for trusted cyber defenders that requires vetting before access is granted. General commercial availability through Google Cloud Vertex AI and AI Studio has not been confirmed on a specific schedule; Google says it will make Argon available as soon as possible.
For software developers and enterprise security teams, Gemini 4 Argon shifts the threat landscape immediately. The model is designed for complex cybersecurity and coding tasks, according to Google, which means engineering teams need to prepare for automated scanning of open-source repositories by threat actors who develop or replicate similar capabilities. IT leaders should evaluate the Fairwind Program now to access defensive capabilities before the gap between defenders and potential adversaries closes.
Why Google Is Restricting Access to Its Own Model
The core capability that makes Argon valuable to defenders also makes it dangerous if broadly released without controls: the system can autonomously identify software vulnerabilities end-to-end, from discovery through suggested patch generation, without human prompting at each step. Google's security blog describes this as a product of reinforcement learning from cybersecurity feedback and automated code execution in a sandboxed environment.
Google’s restricted rollout represents a deliberate commercial strategy. By providing the version without cyber guardrails exclusively to trusted cyber defenders through the Fairwind Program, while planning a safety-filtered general release for developers, Google is using defensive cybersecurity compliance as a differentiation strategy against open-source model alternatives that don’t carry the same access controls.
That dual-track approach raises a governance question competitors haven’t fully resolved either: what happens if the model weights are leaked or if a foreign state actor independently replicates the training methodology? Google’s own model documentation acknowledges dual-use risks, red-team failure rates, and current limitations on guardrails against adversarial prompt injection. The company says its frontier safety evaluation was completed before release, but explicitly notes that no evaluation framework fully eliminates dual-use risk at this capability level.
What the One-Million-Token Context Window Actually Changes
Argon’s one-million-token context window allows it to process large codebases in a single session. Google notes that the system can assist with migrations involving codebases of 800,000 or more lines of code, with automated and manual auditing, emulation testing, and review before production deployment. For a security team auditing a ten-year-old financial system for vulnerabilities, that’s the difference between piecemeal analysis and a comprehensive codebase review in one session.
For organizations that gain Fairwind access, the practical workflow Google describes involves feeding a system’s full codebase, flagging known CVE patterns, and receiving both vulnerability identification and patching code back as outputs.
General commercial users will receive a version with safety filters applied that limit autonomous exploit-generation functionality while preserving the model’s capabilities for coding assistance, document analysis, and general enterprise tasks. The timing of that general release on Vertex AI has not been confirmed as a specific date.
Google’s Gemini model family has moved from general-purpose AI assistant to a system with enough autonomous capability that access decisions have security and geopolitical dimensions beyond typical software releases. For enterprise teams evaluating AI infrastructure risk, understanding how frontier AI cybersecurity tools are licensed and controlled is becoming as important as evaluating the performance benchmarks.
The Fairwind Program application process is available through Google Cloud. General commercial availability on Vertex AI and AI Studio is expected when Google determines the model is ready for broader deployment. Watch for third-party independent security audits, which will provide a benchmark-verified performance picture beyond Google’s own reported figures.